Run a Five Test Deal Room Security POC in 3–7 Days for Sellers
Deal room security means one thing: a buyer-facing decision room ensures each stakeholder only sees what they are authorized to see, with verifiable proof later. The single biggest demand from procurement and security teams evaluating these tools is permission-aware sharing backed by an immutable audit trail. Everything below covers the controls that deliver that, how to test vendor claims in a short proof of concept, and how to run the room once the deal is live.
TL;DR:
- Permission controls must be role-based at the folder, document, and page level, with separate flags for viewing, downloading, and printing, to prevent unauthorized access.
- Audit logs should record every action with timestamps, actors, and IP addresses, and AI integrations must respect permission boundaries to prevent leaks through summaries or content ranking.
- Running a security proof of concept in under a week involves testing permissions, audit export, Q&A, DRM, and AI redaction, with score-based evaluation and external review recommended for thoroughness.
- Integration with existing systems should include SSO, CRM sync, embedded eSignature, and API access, while certifications like SOC 2 and ISO 27001 are minimum standards for data handling security.
- Post-deal, access must be revoked immediately, full audit trails exported, and governance maintained through assigned ownership, regular reviews, and clear incident escalation protocols.
Table of Contents
- What Layered Deal Room Security Controls Actually Look Like
- How to Run a Deal Room Security POC in Under a Week
- Integration, Compliance, and the Trade-Offs Nobody Mentions Upfront
- Running Secure Deal Rooms Across the Deal Lifecycle
- Where Sales Teams Actually Get Deal Room Security Wrong
- How TrailerCast Handles Decision Room Security by Design
- Sources
- FAQ
What Layered Deal Room Security Controls Actually Look Like
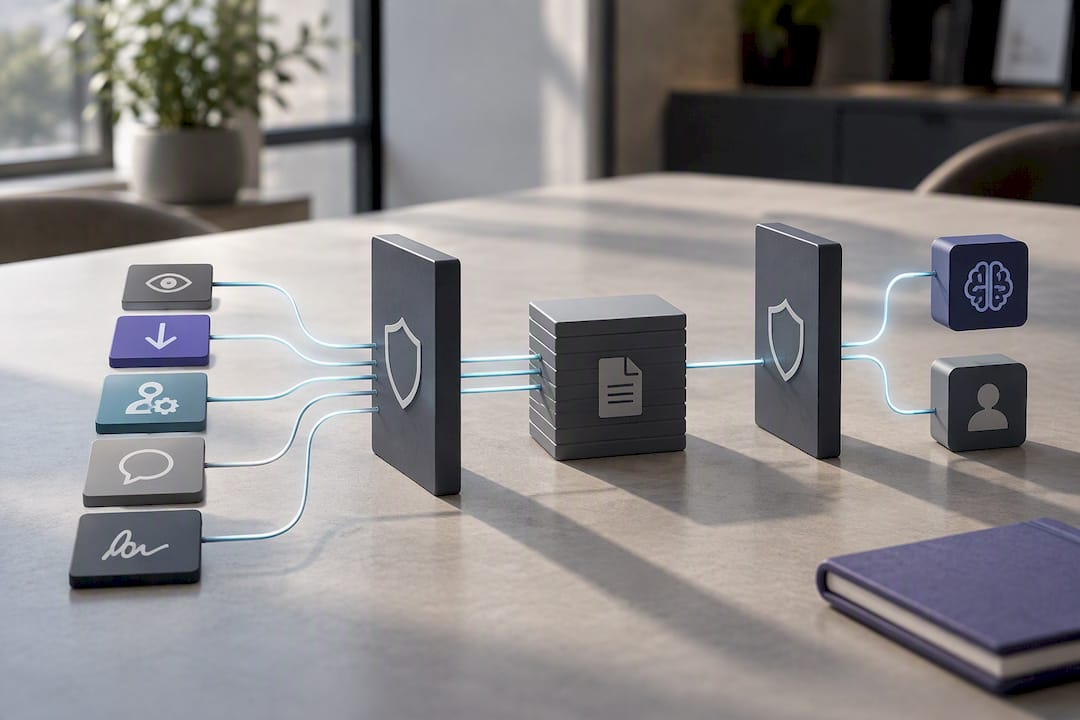
A buyer-facing decision room isn’t a folder with a link. It’s a permission engine wrapped around your demos, docs, and conversation threads, and each layer has to hold up on its own.
Encryption is table stakes, but the details matter. Documents and demo videos at rest should sit behind AES-256, and everything moving between the room and a stakeholder’s browser needs TLS 1.3 in transit. Skip either half and you’ve encrypted the vault but left the delivery truck unlocked.
Identity and authentication come next. SSO/SAML support lets your buyer’s IT team enforce their own login policy instead of trusting a shared password, and MFA closes the gap when a laptop gets stolen or a password gets reused. Domain-restricted access and basic device posture checks add a second gate: a CFO’s corporate email gets in, a personal Gmail forward doesn’t.
Granular permissions are where most tools quietly fail. You need role-based access at the folder, document, and even page level, with separate flags for view, download, and print. Model this around actual buyer roles, not generic tiers:
- Champion: full visibility across discovery, ROI, and documents
- CFO/economic buyer: pricing, ROI model, contract terms, limited technical docs
- CISO/technical evaluator: security documentation, architecture, and Q&A thread, restricted from commercial terms
Document DRM adds a second skin once a file is open: dynamic watermarking tied to viewer identity, expiration dates, and remote revoke if a deal goes cold or a contact changes roles. Watermarking and revoke only govern the room itself. Once a buyer downloads a PDF, that copy is loose, which is exactly why purpose-built decision rooms outperform generic file shares and email that offer no DRM, no expiry, and no revocation at all.
Audit logging closes the loop. Every view, download, print, permission change, Q&A post, and signature event needs a timestamp, an actor, and an exportable record your security team can hand to compliance without translating it first. And if the room uses AI to redact sensitive sections or rank content, that AI has to respect the same permission boundaries as a human viewer — an AI summary that surfaces pricing to a viewer who’s not cleared for it is a leak, not a feature.
How to Run a Deal Room Security POC in Under a Week
Vendor demos show you the happy path. A proof of concept shows you what breaks. Treat the POC as evidence you can attach to an internal risk signoff, not a sales conversation, and you’ll catch the gaps that matter before a real buyer does.
Here’s a five-test structure that fits inside three to seven days:
- Scope it first. Pick four buyer roles, load two or three real documents (a real contract excerpt, not a placeholder PDF), and write down what “pass” looks like for each role before you start clicking.
- Run the permission test. Assign your four roles, carve out one folder exception (say, a CISO-only security packet), and confirm nobody can cross into another role’s view. Then revoke one user mid-test and verify access dies immediately.
- Run the audit test. Perform ten known actions across roles (views, downloads, a permission change, a signature), then export the log and reconcile it against identity, IP address, and timestamp for every action.
- Run the Q&A test. Submit five questions routed to different owners, confirm visibility rules hold (one buyer stakeholder shouldn’t see another’s question thread), and export the full exchange.
- Run the DRM and AI tests. Set a document to expire, confirm the watermark renders correctly, attempt a blocked download or print, then revoke remotely and check the clock. Separately, confirm AI-generated summaries or content rankings never surface material outside the viewer’s permission level.
Score each test pass or fail, not “mostly worked.” A vendor that nails four of five but fumbles remote revoke has a real gap, not a rounding error.
Pro Tip: Bring in a real external reviewer for at least one test, ideally someone outside your company who can act as the buyer would. Internal testers unconsciously avoid the edge cases a real prospect stumbles into.
Integration, Compliance, and the Trade-Offs Nobody Mentions Upfront
The technical controls matter, but a deal room lives inside your stack, not beside it. Before you sign a contract, check how it connects and what it certifies.
Run through this integration checklist during procurement:
- SSO and SCIM support so IT can provision and deprovision users without a manual ticket
- CRM sync that maps room activity back to the right contact and opportunity record
- Embedded eSignature so a signed contract doesn’t require a hop to a separate tool
- API or bulk export access for pulling audit logs into your own retention system
On certifications, SOC 2 Type II and ISO 27001 are the baseline you should expect from any vendor handling buyer documents and engagement data. If your buyers operate under HIPAA or GDPR, ask specifically how the vendor’s data residency and subprocessor list align with those requirements. Ask about backups, too, and what “export everything” looks like at contract termination. A vendor that can’t hand you your own audit trail on exit is a vendor you’ll regret trusting with it in the first place.
There’s a real trade-off between friction and shareability. A no-login link gets forwarded fastest, which is exactly what you want when a champion is multi-threading a deal internally. But no-login also means less identity verification. Domain-restricted access with an NDA click-through, similar to the confidentiality gating used in shared creative or source files, narrows the funnel while keeping a verifiable identity attached to every viewer. Ask your vendor’s support team what their SLA looks like for audit exports and incident response before you need either one.
Pro Tip: Ask for the exit clause in writing before you sign, not after. “We export your data” and “we export your data within five business days in a usable format” are two different guarantees.
Running Secure Deal Rooms Across the Deal Lifecycle
Controls only work if someone operates them consistently. Build this into your RevOps motion, not just your vendor checklist.
Start every deal with a template: a fixed folder structure, a default permission baseline by role, and naming conventions so a CISO packet looks the same whether it’s deal 4 or deal 400. Monitor live activity for anomalies. A sudden burst of downloads from one login, or repeated failed access attempts, deserves a look the same day, not at quarterly review.
At close, run a closeout checklist:
- Revoke external stakeholder access once the contract signs
- Export the full index, audit trail, and Q&A thread for your records
- Preserve any legal holds where required before revoking
Assign clear ownership. RevOps typically owns room configuration and templates, IT owns SSO and provisioning, and legal owns NDA terms and data retention policy. Know your vendor’s escalation contact before an incident, not during one. And no control removes governance responsibility entirely: someone still has to remove dormant users and review access lists on a regular cadence, ideally monthly for active pipeline. Track time-to-revoke and audit-export turnaround as your two core security KPIs.
Where Sales Teams Actually Get Deal Room Security Wrong
The most common failure isn’t a missing control. It’s a leftover one: a CISO packet shared with view access that never gets revoked after the deal closes, or a permission set copied from an old opportunity that quietly grants a new buyer access to a competitor’s pricing sheet.
The deeper problem is fragmentation. When calls, demos, and documents live in five disconnected tools, nobody owns the full permission picture, so people default to email attachments because at least those feel simple. That’s backwards. A room that inherits context from the actual call and demo, rather than starting from a blank folder, is far less likely to get misconfigured because there’s one system tracking who should see what, from the first conversation onward.
— Daniel
How TrailerCast Handles Decision Room Security by Design
Everything in the POC checklist above maps directly to how a modern decision room should work, and it’s worth building that into your evaluation from day one. TrailerCast’s Decision Rooms sit at the center of the deal lifecycle rather than bolted onto the end of it: one branded, no-login room per opportunity, with an attribution tree showing exactly who forwarded what to whom, and a per-stakeholder engagement panel so you can see activity without chasing anyone for an update.
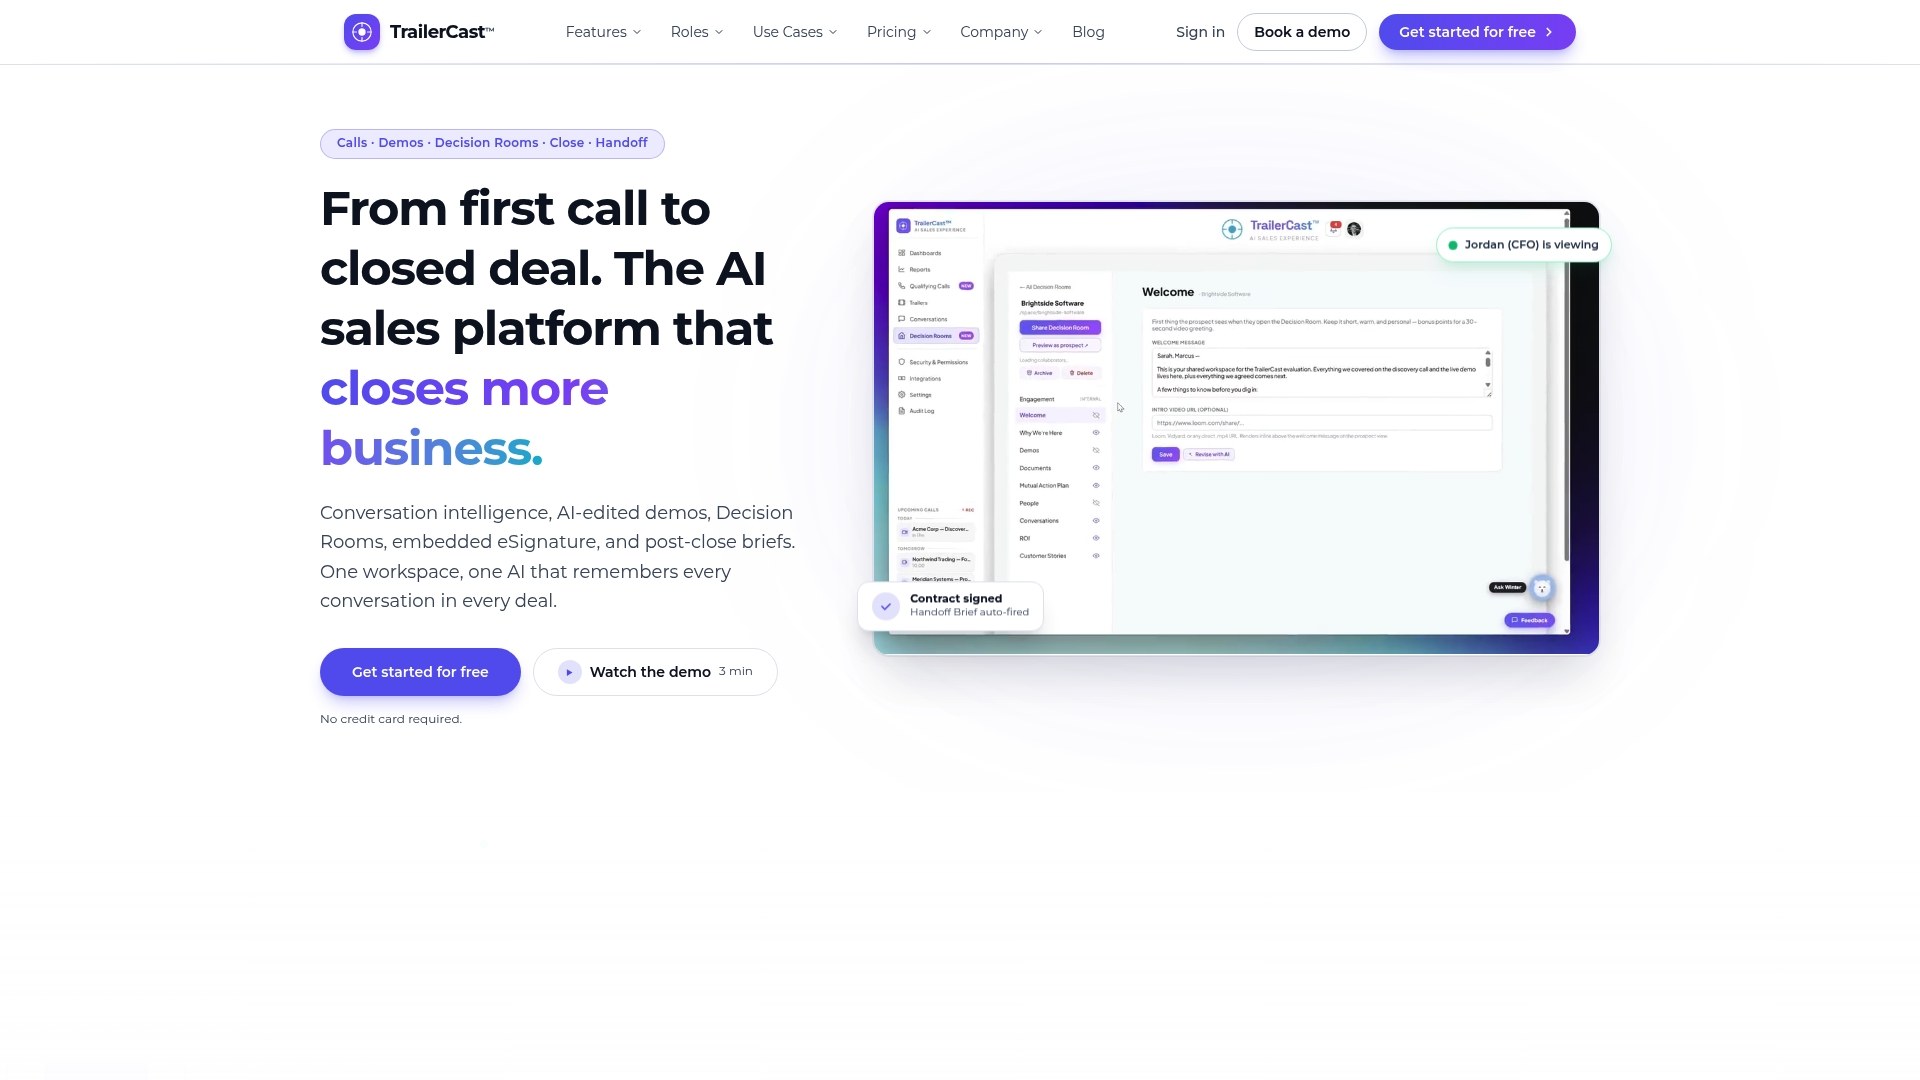
Because the room inherits context from your AI notetaker’s call transcripts and your demo trailers rather than starting from a blank folder, there’s far less temptation to fall back on loose email attachments when a champion needs to loop in a new stakeholder. Contracts close inside the same workspace with embedded eSignature, so the audit trail doesn’t break the moment a deal moves to legal. Review TrailerCast’s security documentation against the permission, audit, and DRM tests above, then start a free trial at $59 per seat per month billed annually to run your own POC before your next renewal decision.
Sources
- Data Room Security 2026 — Encryption, Compliance & Best Practices | SpaceNexus
- Choose the Best Virtual Data Room for Your Deal
- Deal Room Security for Diligence | VeriRFP
- What to Look for in a Due Diligence Data Room
FAQ
What Is Deal Room Security in a Sales Context?
Deal room security refers to the controls that keep a buyer-facing decision room safe: encryption, permission-based access, audit logging, and document protections that let multiple stakeholders view materials without exposing anything outside their role. It’s distinct from due diligence data room security, which serves M&A transactions rather than active sales deals.
How Long Should a Deal Room Security POC Take?
A focused proof of concept can run in three to seven days if you scope it to five specific tests: permissions, audit export, Q&A, DRM, and AI redaction. Trying to test everything at once usually means testing nothing thoroughly.
What Certifications Should a Deal Room Vendor Have?
SOC 2 Type II and ISO 27001 are the baseline certifications to expect from any vendor handling buyer-facing engagement data. If your buyer operates under HIPAA or GDPR, ask how the vendor’s data residency and subprocessor terms align with those frameworks specifically.
Does Dynamic Watermarking Actually Stop Leaks?
Watermarking deters casual forwarding and identifies the source if a document surfaces where it shouldn’t, but it can’t stop someone from screenshotting a screen. Pair it with expiry dates and remote revoke so exposure has a built-in shelf life even after a download.
What Does TrailerCast Cost for a Deal Room?
TrailerCast runs one plan with every feature included, priced at $59 per seat per month billed annually, with a free trial and no credit card required to start.